NIS2 Compliance
Implementing the NIS2 Directive with Asset Transparency Instead of Excel Lists
The NIS2 Directive requires significantly more companies than before to implement effective cyber risk management, ensure prompt reporting, and hold senior management personally accountable. The foundation for all of this is a comprehensive view of your systems, services, and dependencies. DataGerry provides exactly this data foundation and links it to risk assessments, mitigation measures, and evidence.
What is NIS2?
NIS2 is EU Directive (EU) 2022/2555 on strengthening cybersecurity in the European Union. In Germany, it is regulated by the NIS2 Implementation and Cybersecurity Strengthening Act (NIS2UmsuCG), which primarily revises the BSI Act (BSIG). Compared to the previous KRITIS regulation, the number of affected companies in Germany is estimated to rise to around 30,000.
Is your company affected by NIS2?
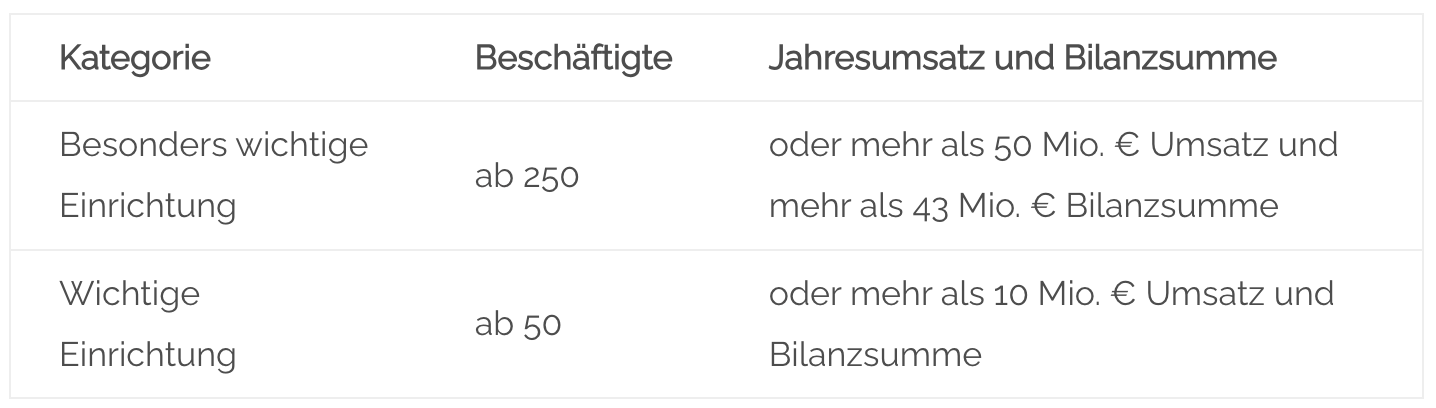
The regulation applies to companies in 18 sectors—ranging from energy, transportation, and healthcare to digital infrastructure, IT services, manufacturing, food, and waste management—provided they meet certain size thresholds:
| Category | Employees | Annual Revenue and Total Assets |
| A particularly important facility | 250 or more | or more than €50 million in revenue and more than €43 million in total assets |
| Important Institution | 50 or more | or more than €10 million in revenue and total assets |
For some organizations, such as certain digital infrastructure providers, NIS2 applies regardless of their size. Affected companies must register with the BSI themselves.
The regulation applies to companies in 18 sectors—ranging from energy, transportation, and healthcare to digital infrastructure, IT services, manufacturing, food, and waste management—provided they meet certain size thresholds:
For some organizations, such as certain digital infrastructure providers, NIS2 applies regardless of their size. Affected companies must register with the BSI on their own.
How does DataGerry help with the implementation of the NIS2 requirements?
Article 21 of the Directive (in Germany, § 30 BSIG) requires appropriate and proportionate risk management measures. Many of these measures require that you know which assets and services you operate and how they are interconnected.
| NIS2 Requirement | How DataGerry Supports This |
| Risk Analysis and Security Concepts | Assess risks directly at the asset and service levels; risk matrix; clearly defined risk owners |
| Security Incident Response | Dependency visualization immediately shows affected services; option to integrate with SIEM/SOC and ticketing systems |
| Business Continuity, Backup, Crisis Management | Identification of critical services as the basis for BIA, emergency, and recovery plans |
| Supply Chain Security | Record service providers and suppliers as objects and link them to the services that depend on them |
| Security in procurement, development, and maintenance, including vulnerability management | Integration of vulnerability scanners; affected assets and services are directly assigned |
| Assessment of the Effectiveness of the Measures | Measure Status, Reports, and Audit Trail as Evidence |
| Access Control and Asset Management | Complete asset inventory with owners; integration with IAM/NAC |
Article 21 of the Directive (in Germany, § 30 BSIG) requires appropriate and proportionate risk management measures. Many of these measures require that you know which assets and services you operate and how they are interconnected.
NIS2 Requirement:
Risk Analysis and Security Concepts
Here’s how DataGerry helps
assess risks directly at the asset and service levels, with a risk matrix and clearly defined risk owners
NIS2 Requirement
: Security Incident Response
Here’s how DataGerry supports
: Dependency visualization immediately shows affected services; option to integrate with SIEM/SOC and ticketing systems
NIS2 Requirement
: Business Continuity, Backup, Crisis Management
This is how DataGerry supports
in identifying critical services as the basis for BIAs, emergency plans, and disaster recovery plans
NIS2 Requirement
: Supply Chain Security
This is how DataGerry helps
service providers and suppliers to record themselves as objects and link them to the services that depend on them
NIS2 Requirement
: Security in Procurement, Development, and Maintenance, Including Vulnerability Management
DataGerry supportsthe integration of vulnerability scanners int
; affected assets and services are assigned directly
NIS2 Requirement
: Assessment of the Effectiveness of Measures
For example, DataGerry supports
compliance status, reports, and audit trails as evidence
NIS2 requirement
: access control and asset management
How DataGerry supports
: Complete asset inventory with owners; integration with IAM/NAC
What reporting requirements apply to NIS2?
Significant security incidents must be reported in several stages:
- Early warning within 24 hours of becoming aware of the incident
- Report with an initial assessment within 72 hours
- Final report no later than one month after the report
If you have to wait until an emergency to investigate which systems depend on a failed component, you’ll lose valuable hours. In DataGerry, dependencies are already documented. You can immediately see which services and customers are affected.
Who is liable, and what fines may be imposed for NIS2 violations?
NIS2 places direct responsibility on senior management: It must approve risk management measures, monitor their implementation, and participate in regular training sessions. Violations may result in fines of up to €10 million or 2% of global annual revenue (for critical infrastructure entities) or up to €7 million or 1.4% (for important infrastructure entities).
5 Steps to NIS2 Implementation with DataGerry
1. Check for impact and register with the BSI
First, determine whether your company is subject to NIS2. The key factors are industry sector, number of employees, revenue, and total assets. If you are subject to the regulation, you must register with the BSI yourself. Document the assessment even if you are not subject to the regulation. This will allow you to substantiate your assessment later.
2. Record Assets and Services
Without a complete inventory, there can be no effective risk management. Set up a CMDB in DataGerry that includes all relevant systems, applications, services, and service providers, or import existing data. Assign an owner to each object and map dependencies—such as which services run on which server or with which cloud provider.
3. Assess Risks
Assess probability and impact directly for the affected asset or service. DataGerry automatically calculates the risk and displays it in a risk matrix. For each risk, designate a risk owner who is responsible for managing it. Be sure to also consider risks from your supply chain.
Check for Impact
Identify assets and services
Assess Risks
Implement and document measures
Establish the ability to report
4. Implement and document measures
Develop specific measures based on the risks and align them with the minimum requirements set forth in Article 21 of NIS2 and Section 30 of the BSIG. Assign the measures to risks and assets, and track their implementation status. The audit trail documents every change. This provides you with reliable evidence for regulatory authorities, auditors, and management.
5. Establish the ability to report
In an emergency, every hour counts. Visualize dependencies so that, in the event of an incident, you can immediately identify which services and customers are affected. Integrate SIEM, ticketing, and vulnerability scanners via OpenCelium, and define who is responsible for making decisions and reporting incidents internally. This makes it realistic to meet the 24-hour deadline for early warning.
FAQ – NIS2 with DataGerry
Are you ready to take control of your data?
Start your 14-day free trial of DataGerry today.
Try DataGerry, the open-source CMDB that brings structure and flexibility to your IT documentation. Discover powerful features, automate your workflows, and gain a complete overview of your assets—with no obligations.
Please feel free to contact us
Contact the DataGerry team
Do you have any questions, or are you facing a particular challenge?
Our dedicated DataGerry team would be happy to assist you.
Office Address
Hauptstraße 8b, 82008 Unterhaching, Deutschland
Email
info@datagerry.com
Phone
+49 89 608668 0
Follow us on